完全な翻訳は近日公開 — 製品詳細は英語、ナビゲーションは日本語で表示しています。
Splunk

Splunk レビュー

Turn scattered machine data into fast security decisions and reliable operations.

Splunkは月額$5 (≈ ¥793)から · 9プラン · 2026年10月13日に価格を確認

著者 Ciroapp Editorial Team · 更新日 2026年9月17日

追加費用なしでコミッションが発生する場合があります

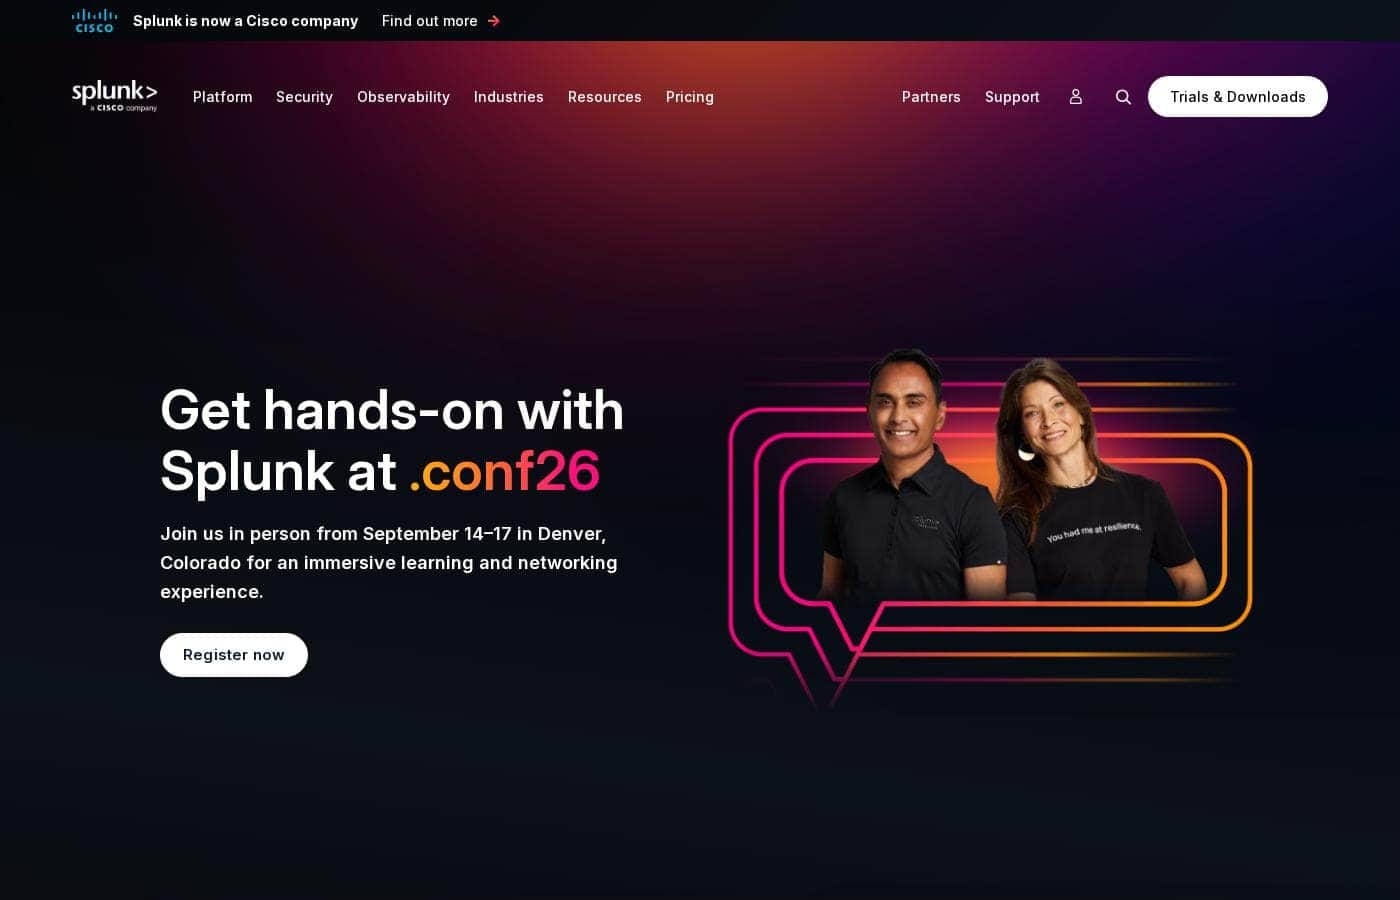
Splunkのホームページスクリーンショット

概要

Splunkの評価、価格概要、主な機能、注目ポイントをすばやく確認できます。
料金確認日 2026年10月13日

Ciroappスコア

4.1/ 5

Splunk unifies petabytes of machine data for security, IT, and AI agent monitoring, with strong customer results like Specsavers' 10x faster MTTR. But its core products hide pricing behind custom quotes, and teams need skilled staff to run it well. Overall, it's a proven enterprise pick if you can absorb the cost and complexity.

長所

  • 長所:Unifies machine data at petabyte scale across security, observability, and networking, with Federated Search that queries sources where they live instead of forcing costly data movement and duplication
  • 長所:Enterprise Security bundles SIEM, SOAR, and UEBA into one platform, and customer-reported results include Carrefour cutting threat response times 3x and Specsavers reporting 10x faster MTTR with 25,000 hours saved monthly
  • 長所:Agent Observability, built on the Galileo acquisition, provides real-time guardrails, traceability, and token-cost attribution for AI agents — a capability most observability platforms don't offer yet

短所

  • 短所:Core platform and security products (Splunk Cloud Platform, Splunk Enterprise, Enterprise Security, SOAR) have no published pricing — everything requires a custom sales quote based on ingest, workload, or activity, making budgeting difficult upfront
  • 短所:The platform's breadth across security, AIOps, APM, and data pipelines demands trained staff or certified admins to operate well, which is a real overhead for teams without dedicated data engineering or security expertise
  • 短所:Ingest- and activity-based pricing can scale sharply with data volume, and while overages only apply to sustained excess, organizations with spiky or growing telemetry need careful capacity planning to avoid cost surprises
最適
  • Enterprise security teams (SOCs) that need SIEM, SOAR, and UEBA in one place
  • IT and SRE teams monitoring apps across cloud, containers, and on-prem
  • Organizations running AI agents that must be monitored, governed, and cost-controlled
無料トライアル
Yes
このセクションは概要です。機能、ユースケース、価格、レビューの詳細は下に続きます。

Splunkとは?

Your logs live everywhere. Security alerts pile up, outages sneak through, and nobody sees the whole picture. Splunk pulls machine data into one platform, so teams detect threats faster, spot issues before users do, and let AI handle repetitive work.

It's built for organizations that can't afford blind spots.

Splunk is a data platform that unifies machine data at petabyte scale across security, observability, and networking. Now part of Cisco, it serves enterprises in finance, healthcare, government, retail, and more. Security teams use it to detect and respond to threats.

IT teams use it to monitor apps and infrastructure. It's aimed at organizations that need to search huge data volumes in real time and act on them with AI.

Splunkを選ぶべきですか?

プラン比較や公式サイトへ進む前に確認したい購入判断のポイントです。

選ぶべき人

  • Teams that want faster threat detection and incident response, backed by customer-reported results like 3x faster response times
  • Businesses that need petabyte-scale search without moving or duplicating data
  • Shops already using OpenTelemetry or wanting 2,000+ prebuilt integrations
  • Enterprises that prefer vendors recognized as leaders by major analyst firms
  • Organizations willing to invest in training to build internal expertise

避けるべき人

  • Small teams with basic logging needs — the platform's depth and enterprise focus may be more than you require
  • Buyers who need published pricing — numbers aren't listed on the site, so you'll need to talk to sales for a quote
  • Teams without data engineering or security expertise — pipelines, detections, and integrations take skilled people to run well
  • Anyone cautious about vendor changes — Splunk is now part of Cisco, so its roadmap sits inside a larger company

購入前の次のステップ

  1. 1Estimate your data volume and sources first — Splunk's architecture and costs scale with data, so sizing matters before you commit.
  2. 2Take the free interactive product tours for Splunk Cloud Platform, Enterprise Security, and Infrastructure Monitoring to judge the interface.
  3. 3Start a free trial or download to test against a sample of your real data.
  4. 4Browse Splunkbase to confirm integrations exist for your current tools, including any OpenTelemetry setups.
  5. 5Contact sales for a quote, since pricing isn't published, and ask about support programs and training options.

使いやすさ

Splunk's site points to a deep, enterprise-grade platform rather than a quick-install tool. On the plus side, there are free trials, interactive product tours, extensive documentation, training and certification paths, and a large community with Splunk Answers. Those resources help new teams ramp up. Still, the breadth — security, AIOps, application monitoring, and data pipelines — suggests you'll want trained staff or certification to get full value.

Splunk 主な機能

✨ One home for all your machine data

Logs, metrics, and traces usually live in separate silos, and that's where problems hide. Splunk unifies machine data at petabyte scale across security, observability, and networking. With Federated Search, you query sources where they live — no ingest tax, no unnecessary data movement.

Your teams and AI get real-time context across domains.

🛡️ Defend at machine speed

AI-powered attacks shrink remediation windows from months to minutes. Splunk Enterprise Security unifies threat detection, investigation, and response in one AI-powered SecOps platform. It brings together:

  • SIEM to detect and stop threats
  • SOAR to accelerate and automate response
  • UEBA to spot user and entity anomalies

Your experts stay in control while agents handle the repetitive work.

✨ Spot issues before your users do

Observability Cloud gives you real-time visibility across any environment. Application Performance Monitoring troubleshoots slow code. Infrastructure Monitoring watches clouds, containers, and on-prem systems.

Digital Experience Analytics shows how users actually feel performance. When something breaks, AI SRE agents isolate root causes and suggest targeted fixes like rollbacks or capacity adjustments.

✨ Keep your AI agents in check

Autonomous agents can take unpredictable, unauthorized actions. Splunk Agent Observability, powered by the Galileo acquisition, lets you observe and secure AI agents, models, and infrastructure. Real-time guardrails and traceability help prevent drift, hallucinations, and data leakage.

Token usage tracking with full attribution keeps AI costs from running away.

✨ Build custom AI on your own data

Sometimes off-the-shelf AI isn't enough. The AI Toolkit helps you build, test, and deploy custom AI for your operations. The Splunk MCP Server connects AI tools to Splunk data securely.

Together, they power resilient agentic operations built on real-time context from your own environment.

使用例

🛡️ Detect and respond to threats faster

Security analysts drown in alerts from scattered tools. Splunk Enterprise Security unifies SIEM, SOAR, and UEBA, so your team spots insider threats, automates playbooks, and acts fast. Carrefour cut threat response times 3x.

Expected outcome: incidents remediated in minutes, not hours.

📡 Spot issues before users do

IT and SRE teams watch apps across cloud, containers, and on-prem. Splunk Observability Cloud correlates alerts and isolates root causes fast. Specsavers reports 10x faster MTTR and 25,000 hours saved monthly.

Tip: Start with Infrastructure Monitoring at $15/host/month.

🤖 Govern AI agents and costs

Teams deploying AI agents worry about drift, hallucinations, and surprise bills. Agent Observability adds real-time guardrails, traces agent actions, and tracks token spend. You keep autonomy without losing control.

Expected outcome: clear visibility into agents, models, and costs.

🔍 Search data where it lives

Data teams fight sprawl and rising ingest costs. Federated Search processes telemetry at petabyte scale without moving it, so you keep full context and skip the ingest tax.

Tip: Check Splunkbase first — 2,000+ integrations plus native OpenTelemetry support.

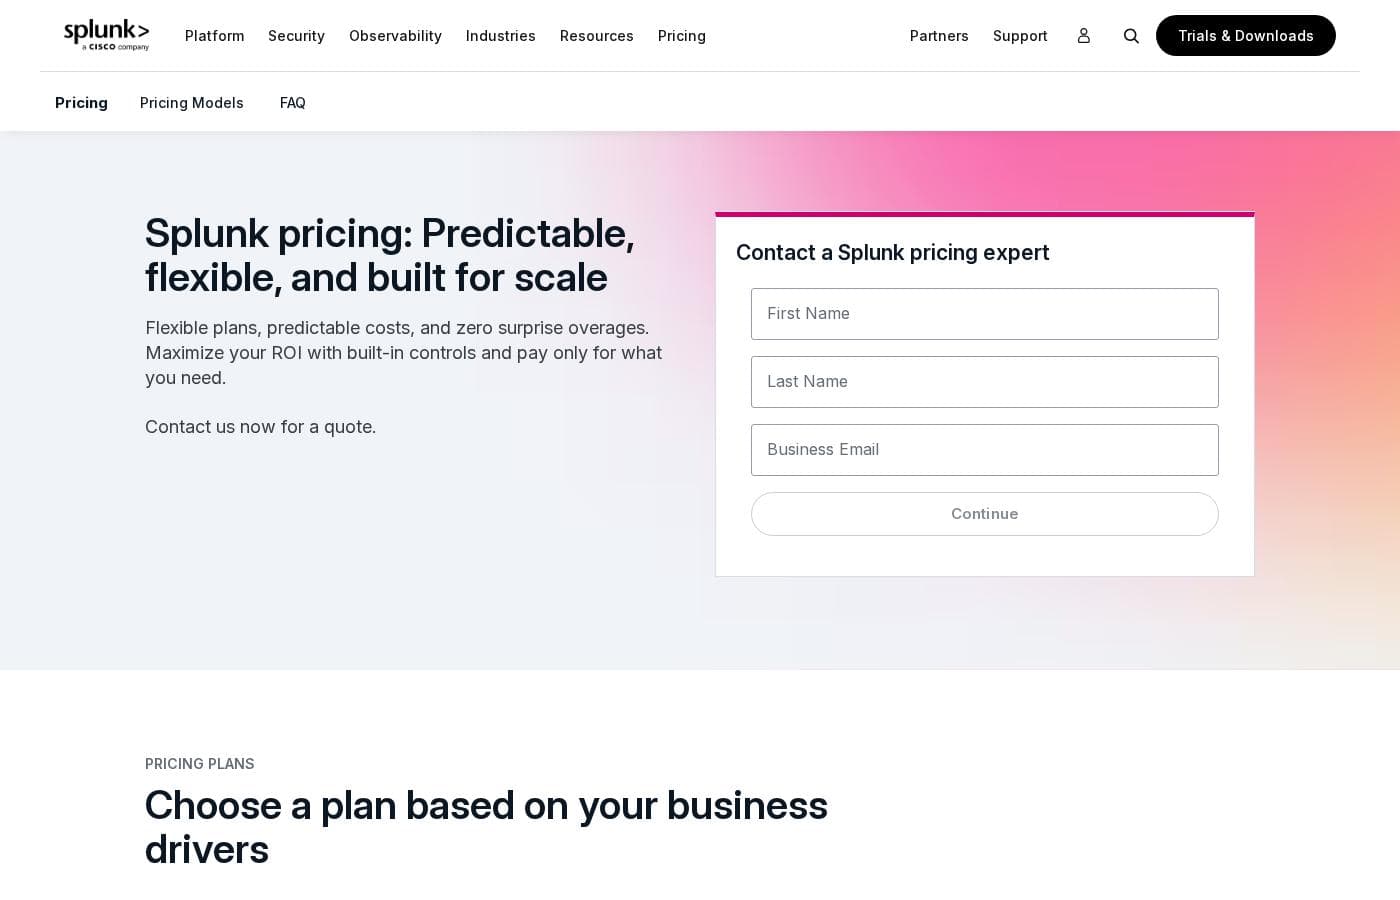
Splunkの料金

最安$5/月≈ ¥793

  • 9プラン

2026年10月13日に次のページで価格を確認: Splunkの料金ページ

Splunkの料金ページのスクリーンショット料金ページのスクリーンショットを見る
プラン月払い年払い含まれる機能
Splunk Observability Cloud – Infrastructure
1ユーザーあたり
—
$15/月
≈ ¥2,379
年額$180
  • Infrastructure Monitoring
  • Log Observer Connect
  • Network Explorer
  • Synthetic Uptime Monitoring
Splunk Observability Cloud – App & Infra
1ユーザーあたり
—
$60/月
≈ ¥9,516
年額$720
  • Everything in Infrastructure
  • APM with Always On Profiling
  • Synthetic API Monitoring
Splunk Observability Cloud – End-to-End
1ユーザーあたり
—
$75/月
≈ ¥11,895
年額$900
  • Everything in App & Infra
  • Real User Monitoring
  • Synthetic Browser Monitoring
  • Database Monitoring and Secure Application as optional add-ons
Splunk AppDynamics – Infrastructure Edition
—
$6/月
≈ ¥952
年額$72
  • Infrastructure Monitoring
  • Add-ons available separately
Splunk AppDynamics – Premium Edition
1ユーザーあたり
—
$33/月
≈ ¥5,234
年額$396
  • Application Performance Monitoring
  • Database Monitoring
  • Log Observability
Splunk On-Call
1ユーザーあたり
Starts at $5 per user/month (billed annually)
$5/月
≈ ¥793
年額$60
Starting price covers up to 10 seats
  • 100+ IT service management integrations
  • On-call schedules and escalation policies
  • Faster incident remediation
Splunk Cloud Platform
公式サイトを参照
公式サイトを参照
  • Unlimited users
  • Scales to petabytes of data
  • Cloud Flex spend reallocation
  • Eligible Cisco telemetry at 0.5x weighted ingest rate
Splunk Enterprise
公式サイトを参照
公式サイトを参照
  • Unlimited users
  • On-prem, private cloud, or air-gapped deployment
  • Eligible Cisco telemetry at 50% weighted ingest rate
Splunk Enterprise Security
公式サイトを参照
公式サイトを参照
  • Essentials and Premier editions
  • Both include SIEM, threat intelligence, Detection Studio, and Exposure Analytics
  • Premier adds SOAR, UEBA, and Automated Threat Analysis

2026年10月12日のECB参照レートで換算しています。ベンダーの現地価格は異なる場合があります。

価格の推移

2026年10月1日から価格を追跡中。まだ価格変更はありません。

価格タイプ: Free plan, Free trial, Yearly subscription, Per seat pricing, Usage-based pricing

料金に関する補足

Splunk prices most of its platform and security products through custom quotes based on ingest, workload, or activity. Published rates start at $5/user/month for On-Call, $15/host/month for Observability Cloud, and $6/vCPU/month for AppDynamics, all billed annually, with free trials and a free Observability edition available.

Splunk's published prices range from $5 to $75 per month, billed annually, while its core Platform and Security products are priced by custom quote.

Here's how each product and tier breaks down.

Splunk Observability Cloud – Infrastructure

Price: Starts at $15 per host/month, billed annually Best For: Teams monitoring infrastructure and cloud services Other Features:

  • Infrastructure Monitoring
  • Log Observer Connect
  • Network Explorer
  • Synthetic Uptime Monitoring

This is the entry point into Observability Cloud. It's a good fit if you mainly want visibility into servers, containers, and cloud services without paying for app-level tooling.

Splunk Observability Cloud – App & Infra

Price: Starts at $60 per host/month, billed annually Other Features:

  • Everything in Infrastructure
  • APM with Always On Profiling
  • Synthetic API Monitoring

Pick this tier when application performance matters as much as infrastructure health. It adds troubleshooting for both cloud-native and monolithic apps.

Splunk Observability Cloud – End-to-End

Price: Starts at $75 per host/month, billed annually Other Features:

  • Everything in App & Infra
  • Real User Monitoring
  • Synthetic Browser Monitoring
  • Database Monitoring and Secure Application available as optional add-ons

This is the full-package tier for teams that also want user-session visibility. If you only need infrastructure metrics, the lower tiers will cost far less.

Splunk AppDynamics – Infrastructure Edition

Price: Starts at $6 per vCPU/month, billed annually Other Features:

  • Infrastructure Monitoring
  • Add-ons available separately

This edition suits teams that want AppDynamics' monitoring foundation at the lowest listed cost.

Splunk AppDynamics – Premium Edition

Price: Starts at $33 per host/month, billed annually Other Features:

  • Application Performance Monitoring
  • Database Monitoring
  • Log Observability

Premium makes sense when you need to tie hybrid and on-prem app performance to business impact.

Splunk AppDynamics – Enterprise Edition

Price: Starts at $50 per host/month, billed annually Other Features:

  • Everything in Premium
  • Transaction Analytics
  • Add-ons: Application Security ($13.75/month per CPU core), Real User Monitoring ($0.06 per 1,000 tokens), Browser Synthetics ($12 per test location), SAP ($95 per CPU core)

Go Enterprise if transaction analytics across complex business applications is a must-have.

Splunk On-Call

Price: Starts at $5 per user/month, billed annually (up to 10 seats) Best For: Small teams managing on-call schedules Other Features:

  • 100+ IT service management integrations
  • Streamlined escalation policies
  • Free trial available

This is the most accessible way in. It routes incidents to the right person fast, so nothing sits unresolved. 🎯

Splunk Cloud Platform

Price: Custom quote (activity-based, ingest, or workload pricing) Other Features:

  • Unlimited users
  • Scales to petabytes of data
  • Cloud Flex lets you shift spend across Splunk products
  • Eligible Cisco telemetry counts at a 0.5x weighted ingest rate
  • Free trial available

Splunk Enterprise

Price: Custom quote (data-ingest or workload pricing) Other Features:

  • Unlimited users
  • Runs on-prem, in private cloud, or in air-gapped environments
  • Eligible Cisco telemetry counts at a 50% weighted ingest rate
  • Free trial available

Splunk Enterprise Security

Price: Custom quote (activity-based, workload, or ingest pricing) Other Features:

  • Two editions: Essentials and Premier
  • Both include SIEM, threat intelligence, Detection Studio, and Exposure Analytics
  • Premier adds SOAR, UEBA, and Automated Threat Analysis

Essentials is built for human-led, AI-accelerated defense. Premier targets teams ready for adaptive, autonomous security operations.

Trials and buying: Splunk offers a free edition of Observability Cloud, plus free trials for Cloud Platform, Enterprise, SOAR, AppDynamics, and On-Call — though trial length isn't published on the pricing page. Every purchase includes standard support, and volume discounts are available. There's no money-back guarantee listed, so confirm your license limits and expected data volumes with a Splunk expert before committing.
コスト計算ツール

チームでSplunkを使う場合の費用を試算します。

支払い方法

Splunk Observability Cloud – Infrastructureにはこの支払いサイクルの公開価格がありません。

Splunk Observability Cloud – Infrastructureはユーザー単位の料金です:価格 × 5ユーザー。 公開されている定価に基づく概算です(税・アドオン・割引は含みません)。

Splunkを安く使う方法

  • 無料トライアルがあります。支払う前に試しましょう。
  • 一部のプランはユーザー単位の料金です。実際に使う人数分だけ支払いましょう。
無料トライアルを始める

Splunkの価格が変わったらメールで通知

ベンダーの料金ページで価格の変更を検出したときに1通のメールを送ります。ニュースレターやセール情報はありません。ワンクリックで解除できます。

ユーザーレビュー

まだレビューがありません。

レビューを書く

Splunkのレビューを書く
0/100文字
0/2000文字

Splunkを使う理由は?

When minutes matter, waiting on scattered logs isn't an option. Splunk turns machine data into fast, governed action across your whole operation. Based on the company's site and customer stories, here's what stands out:

  • Proven speed gains. Specsavers reports 10x faster MTTR and 25,000 hours saved monthly. Singapore Airlines detects issues 75%+ faster. Carrefour cut threat response times 3x.
  • Scale without silos. Search and process telemetry where it lives, at petabyte scale, to reduce data movement and avoid unnecessary ingest costs.
  • AI that works for you. Agentic SOC tooling, AI SRE agents, and Agent Observability help teams respond at machine speed while governing agent behavior and tracking token costs.
  • Deep ecosystem. 2,000+ apps and integrations on Splunkbase, with native OpenTelemetry support, SDKs, and agents.
  • Analyst-backed trust. Recognized by global analyst firms as a leader in security and observability, and used by the US Department of Defense, Nasdaq, and Coca-Cola.
  • Try before you buy. Free trials, downloads, and interactive product tours let you evaluate the platform against your own needs.

Splunk の代替ツール

ビジネスインテリジェンスカテゴリの他のツール

ビジネスインテリジェンスの全ツールを見る
ElevateForward.ai

ElevateForward.ai

Business Intelligence3.8/5

戦略の診断から計画、実行までを1つのAIプラットフォームで

DataHawk

DataHawk

Business Intelligence3.7/5

AmazonとWalmartの数値を1つのプラットフォームで——変化の理由をAIが解説します。

Tradify

Tradify

Home Service Management Platform4.1/5

Tradify is an all-in-one job management app for trade businesses. It covers the full job lifecycle — inquiries, quoting, scheduling, job tracking, invoicing, and payments — in one place. It's aimed at electricians, plumbers, gas engineers, HVAC techs, and property maintenance services, from sole operators to larger teams. A 14-day free trial is available, and no credit card is required to start.

Backlog by Nulab Inc

Backlog by Nulab Inc

Project Management4/5

Backlog is the all-in-one project management platform built for teams that move fast. It helps small and mid-sized teams manage projects, track bugs, and collaborate across roles without the complexity of enterprise tools.

Goflow

Goflow

Multi-Channel Ecommerce3.9/5

Goflow is a global leader in Multichannel Operating System (MCOS) that enables ecommerce sellers to manage their channel orders, shipping, inventory, listings, transfers, purchasing, forecasting, and analytics from a single interface.

FlowMattic

FlowMattic

Automation4.2/5

FlowMattic is a powerful automation tool trusted by over 7,582 WordPress professionals worldwide. It helps businesses manage their vital operations effortlessly. The platform acts as an essential, reliable, and future-proof tool for anyone running a business on WordPress. Users find that it easily replaces other complex automation systems thanks to its seamless integration. ✅ Whether you run an agency, an e-commerce store, a SaaS platform, or an educational platform, FlowMattic provides the dedicated automated workflows needed for sustainable growth.

Integrately

Integrately

Automation3.9/5

Integrately is a simple and powerful platform designed to hook up your favorite business tools quickly and efficiently. It’s perfect for anyone needing to automate routine tasks without complex coding knowledge. The platform integrates with a vast ecosystem of over 1400 apps, including major players like Pipedrive, Hubspot, Trello, and Google Sheets. The core benefit rests on its massive library of Ready Automations ✨. You don't have to build intricate workflows from the start. Instead, you select a pre-built pathway, connect your accounts, and the automation is instantly ready to boost your productivity.

Volza

Volza

WordPress Plugins4/5

Volza is a global trade-intelligence platform providing verified international trade information and actionable market insights. With over 30 years of expertise in trade analytics, we support thousands of businesses and leading consultancies around the world.

1〜25ユーザー向けの最安ビジネスインテリジェンスソフトウェア

Splunk よくある質問

Splunkの料金はいくらですか?

Splunkの最も安い有料プラン「Splunk On-Call」は月額$5 (≈ ¥793)です。 有料プランは月額$5から$75までです。 2026年10月13日にベンダーの料金ページで価格を確認しました。

Splunkに無料トライアルや返金保証はありますか?

Splunkには無料トライアルがあります。

Splunkの価格は最近変わりましたか?

いいえ。2026年10月1日に追跡を始めて以来、価格の変更は検出されていません。

Will I get surprise overage bills if my data volume spikes?

Splunk only charges overages when you consistently exceed your purchased ingestion or storage capacity. You can monitor usage in real time and adjust allocations through the Splunk Support Portal.

Can I shift my budget between different Splunk products after buying?

Yes. Cloud Flex lets you reallocate spend across the Splunk portfolio — Platform, Security, Observability, AI, Storage, and Federated Search — without restarting procurement.

Do Splunk plans include technical support, and can I get a discount?

Every purchase includes standard support with all major and minor software updates. Premium support is available, and volume discounts are offered — ask a Splunk pricing expert for details.

Splunkを試してみる準備はできましたか?公式サイトまたは価格をご覧ください。

Splunkの担当者ですか? この掲載を申請する · バッジを入手