Sonatype

Sonatype review

Develop faster with less risk, powered by unmatched open source intelligence.

By Ciroapp Editorial Team · Updated Sep 17, 2026
Sonatype homepage screenshot

At a glance

Quick overview for Sonatype: rating, pricing summary, key features, and highlights.
Vendor page checked Oct 23, 2026

Ciroapp score

4.1/ 5

Sonatype brings fast, accurate open source intelligence, claiming 10% more vulnerability coverage than rivals with a 0.1% false positive rate, and blocks malware and risky AI models before they reach your build. Enterprise pricing can climb to $14,028 a month, though, and value depends on real CI/CD integration. Overall, it's a solid pick for teams managing heavy open source and AI dependency loads.

Pros

  • Detects 10% more open source vulnerabilities than competing solutions, expanding coverage against real threats
  • Very low 0.1% false positive rate, so security teams spend less time chasing non-issues
  • Delivers threat intelligence roughly 10X faster than the National Vulnerability Database

Cons

  • Top-tier plans can be expensive, with pricing reaching up to $14,028 per month for larger deployments
  • The breadth of features and policy configuration may require dedicated onboarding effort for smaller teams without dedicated security staff
  • Deep value depends on teams actually integrating it into CI/CD workflows; organizations with fragmented build processes may see slower time-to-value
Best for
  • Application security teams at mid-size to large organizations that need faster, more accurate open source vulnerability intelligence than public databases provide
  • Engineering organizations with heavy open source dependency usage that need automated governance across 50+ languages and formats
  • Teams adopting AI models from public repositories that want to block risky or malicious components before they enter the build
This section is a summary. Detailed sections about features, use cases, pricing, and reviews follow below.

What is Sonatype?

Managing open source dependencies and AI models at scale brings real headaches: dependency sprawl, quality issues, and security risks. Sonatype tackles this by helping teams make smarter, safer decisions from the start. You get to move faster with fewer interruptions, less rework, and built-in security.

✨

Sonatype is a software supply chain management platform. It's built for developers and application security teams who need to securely manage open source and AI components. The platform provides intelligent guidance to choose the best libraries and block malicious code.

💡
Should you choose Sonatype?

Quick buyer guidance before you compare plans or click through.

Choose it if

  • Application security teams at mid-size to large organizations that need faster, more accurate open source vulnerability intelligence than public databases provide
  • Engineering organizations with heavy open source dependency usage that need automated governance across 50+ languages and formats
  • Teams adopting AI models from public repositories that want to block risky or malicious components before they enter the build
  • Platform and DevOps teams looking to reduce remediation and rework by enforcing dependency policies automatically in CI/CD

Skip it if

  • Hobbyists or solo developers with a handful of dependencies who may find enterprise supply chain governance more than they need, even on the free tier
  • Organizations with no dedicated security function that lack the resources to act on policy violations and threat intelligence the platform surfaces
  • Teams whose entire stack is proprietary in-house code with minimal open source or AI component usage, where supply chain security is a smaller concern

Next steps before buying

  1. 1Visit sonatype.com and review the product pricing page to compare the free plan against paid tiers and identify which features your team needs
  2. 2Start with the $0/month plan to connect a repository or build pipeline and see how vulnerability detection and malware blocking perform on your actual dependencies
  3. 3Define your initial governance policies — such as blocking known malware, flagging critical vulnerabilities, and enforcing license rules — before rolling out to all teams
  4. 4Integrate Sonatype into your CI/CD workflow for your highest-risk projects first, then expand coverage across languages and repositories based on results

Sonatype Key Features

✨ Open Source Vulnerability Detection

Sonatype's intelligence engine identifies 10% more open source vulnerabilities than competing solutions, with a verified 0.1% false positive rate. Security intelligence arrives roughly 10 times faster than the National Vulnerability Database, so teams learn about dangerous components before exploits spread rather than after.

✨ Open Source Malware and Risky AI Model Blocking

The platform actively blocks open source malware and risky AI models at the repository perimeter. Instead of relying solely on post-hoc scanning, Sonatype prevents malicious packages and unvetted AI components from ever entering your build pipeline, reducing the chance that poisoned dependencies reach production.

✨ Automated Dependency Governance

Sonatype automates governance of open source dependencies by applying configurable policies across the software supply chain. Teams can enforce license, security, and quality standards automatically, which cuts down on manual remediation, rework, and the back-and-forth between developers and security reviewers.

✨ Broad Language and Tool Integrations

The platform integrates with the tools developers already use and supports 50+ languages and package formats. This means coverage spans Java, Python, JavaScript, and beyond, and security checks fit into existing CI/CD workflows rather than requiring teams to change how they build software.

✨ Component Selection Guidance

Beyond flagging problems, Sonatype provides intelligent guidance for choosing the best libraries upfront. Developers get data on component health, popularity, and risk, helping them pick dependencies that are less likely to become liabilities later in the project lifecycle.

Use Cases

💡 Securing the Software Supply Chain

Security teams use Sonatype to defend against malicious open source packages and compromised AI models. By blocking known malware at the repository level and surfacing vulnerabilities faster than public databases, the platform shortens the window between a threat emerging and your team knowing about it.

💡 Managing Dependency Sprawl in Large Codebases

Organizations with hundreds of applications and thousands of transitive dependencies use Sonatype to bring order to their open source usage. Automated policies flag outdated, vulnerable, or license-problematic components across projects, giving platform teams a single view of supply chain risk.

💡 Governing AI Model Adoption

As teams increasingly pull AI models from public repositories, Sonatype extends supply chain controls to cover these components. Risky or unvetted AI models can be blocked before they enter the build, letting engineering organizations adopt AI tooling without opening a new attack surface.

💡 Reducing Rework for Development Teams

Developers use Sonatype's component guidance to choose healthier libraries at design time, avoiding the cost of swapping out problematic dependencies mid-project. Fewer false positives and earlier insights mean less time chasing ghosts and more time shipping features.

Sonatype pricing

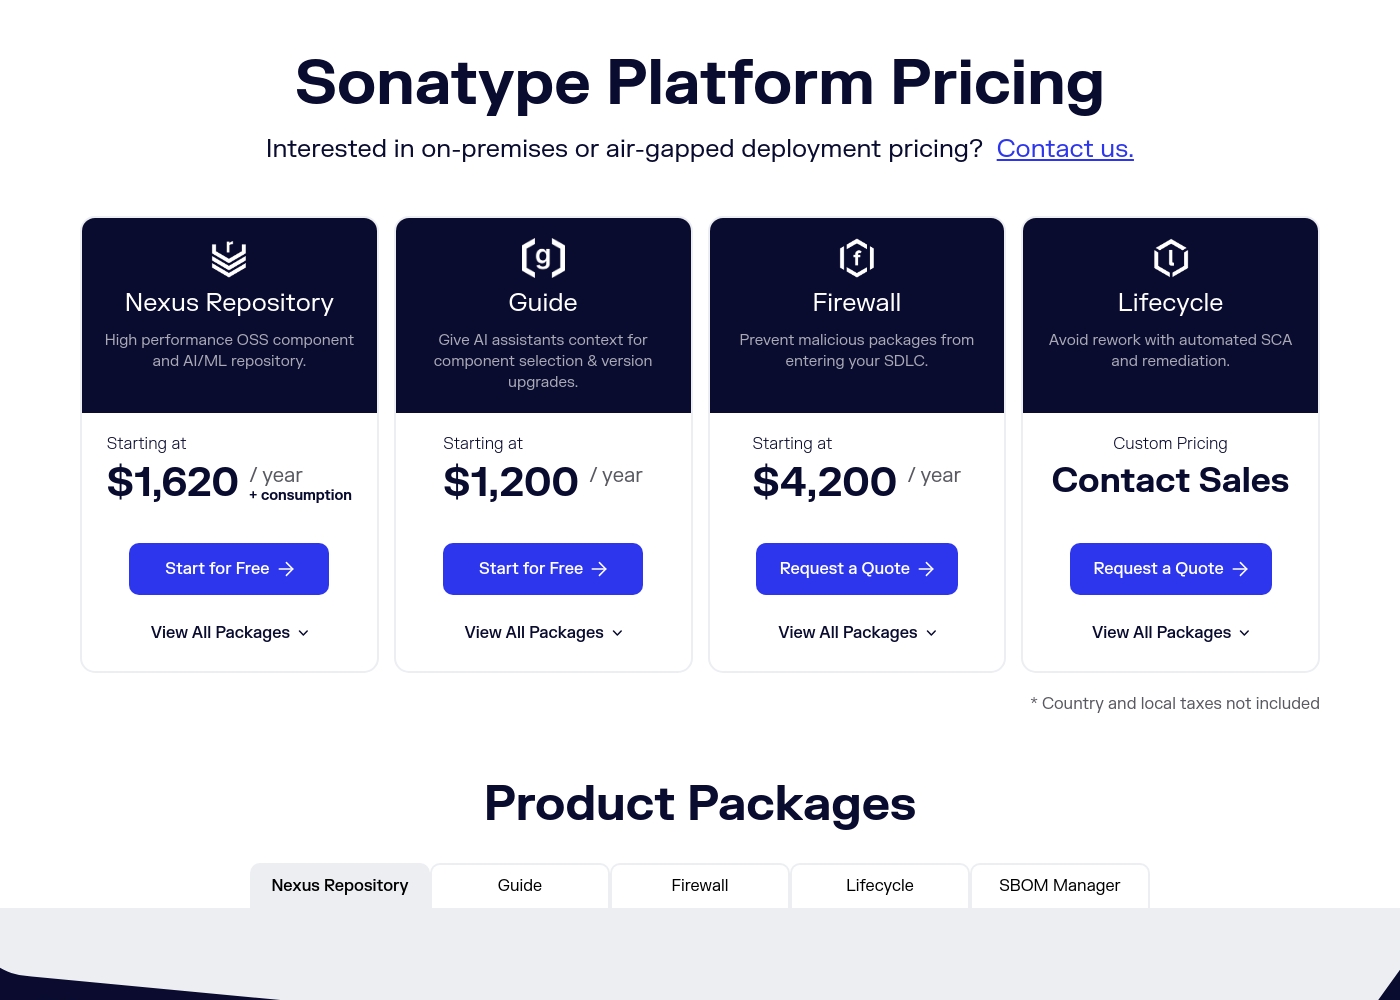
Prices not verified yet — see the vendor page.

Sonatype's pricing page

Sonatype pricing page screenshotView pricing page screenshot

Price history

Tracking prices since Oct 1, 2026. No price change detected yet.

Pricing types: Free plan, Monthly subscription, Yearly subscription, Usage-based pricing

Pricing notes

Sonatype pricing: Plans from $0/month Billing options: Free plan, Monthly subscription, Yearly subscription, Usage-based pricing

Email me when Sonatype changes price

One email when we detect a price change on the vendor's pricing page. No newsletter, no deals. Unsubscribe in one click.

User Reviews

No reviews yet.

Write a Review

Write a Review for Sonatype
0/100 characters
0/2000 characters

Why use Sonatype?

Ready to ship secure code faster? Sonatype gives your team a powerful edge.

  • Discover More Real Threats: They find 10% more open source vulnerabilities than alternatives. ✅
  • Trust the Results: A tiny 0.1% false positive rate means fewer wasted hours chasing ghosts.
  • Get Ahead of Problems: Insights arrive 10X faster than the National Vulnerability Database.
  • Automate Your Governance: Manage dependencies and policies to reduce remediation and rework.
  • Protect Your Perimeter: Actively block open source malware and risky AI models from your repository.
  • Work Your Way: Integrates with your favorite tools across 50+ languages and formats.

Sonatype alternatives

Other tools in the Software Composition Analysis category

View all Software Composition Analysis tools
SOOS

SOOS

Software Composition Analysis1/5

SOOS is an integrated software security platform designed for engineering, security, and compliance teams managing open-source risk. It helps you identify vulnerabilities and license issues deep in your app's dependency tree and provides a unified view to monitor risk and stay compliant.

Sonatype FAQ

Does Sonatype offer a free plan or trial?

Yes. Sonatype's pricing starts at $0 per month, with a free plan available alongside monthly, yearly, and usage-based subscription options.

What languages and ecosystems does Sonatype support?

Sonatype supports 50+ languages and package formats and integrates with the tools your team already uses across the development lifecycle. This broad coverage means it can secure dependencies in ecosystems like Java, Python, and JavaScript within a single governance framework rather than requiring separate tools per language.

How is Sonatype different from just using the National Vulnerability Database?

Sonatype delivers vulnerability intelligence roughly 10 times faster than the NVD and finds about 10% more open source vulnerabilities than alternatives, with a 0.1% false positive rate. Beyond detection, it goes further than a public database by actively blocking malware and risky AI models at your repository and automating policy enforcement, so risks are prevented rather than merely reported.

Who should use Sonatype?

Sonatype is built for developers and application security teams that rely heavily on open source and AI components. It is particularly valuable for organizations that need to manage dependency sprawl, enforce consistent security and license policies across many projects, and defend against malicious packages entering their software supply chain.

Ready to try Sonatype? Check out the official site or pricing.

Are you Sonatype? Claim this listing · Get the badge